Wed 15 Apr 2026 ▪
4
min read ▪ by
Summarize this article with:
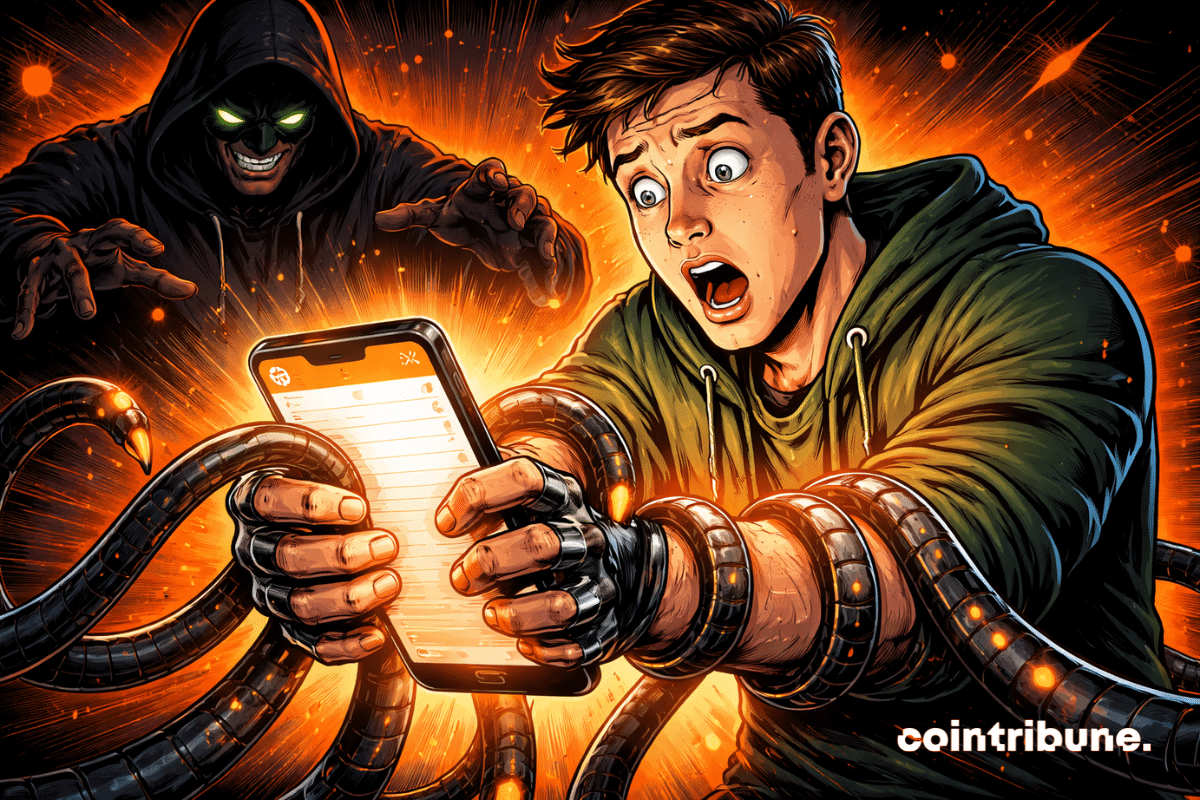
Cybercriminals are not lacking in imagination. This time, they turned a simple note-taking application into a silent weapon to empty the crypto wallets of their targets. And the worst part? The victim sees nothing coming.
In Brief
- Scammers use the Obsidian app to deploy malware via trapped community plugins.
- Victims are recruited on LinkedIn and Telegram, under cover of a fake venture capital company.
- An unprecedented Trojan horse, named PHANTOMPULSE, takes full control of the infected device.